01
Your keys (BYOK)
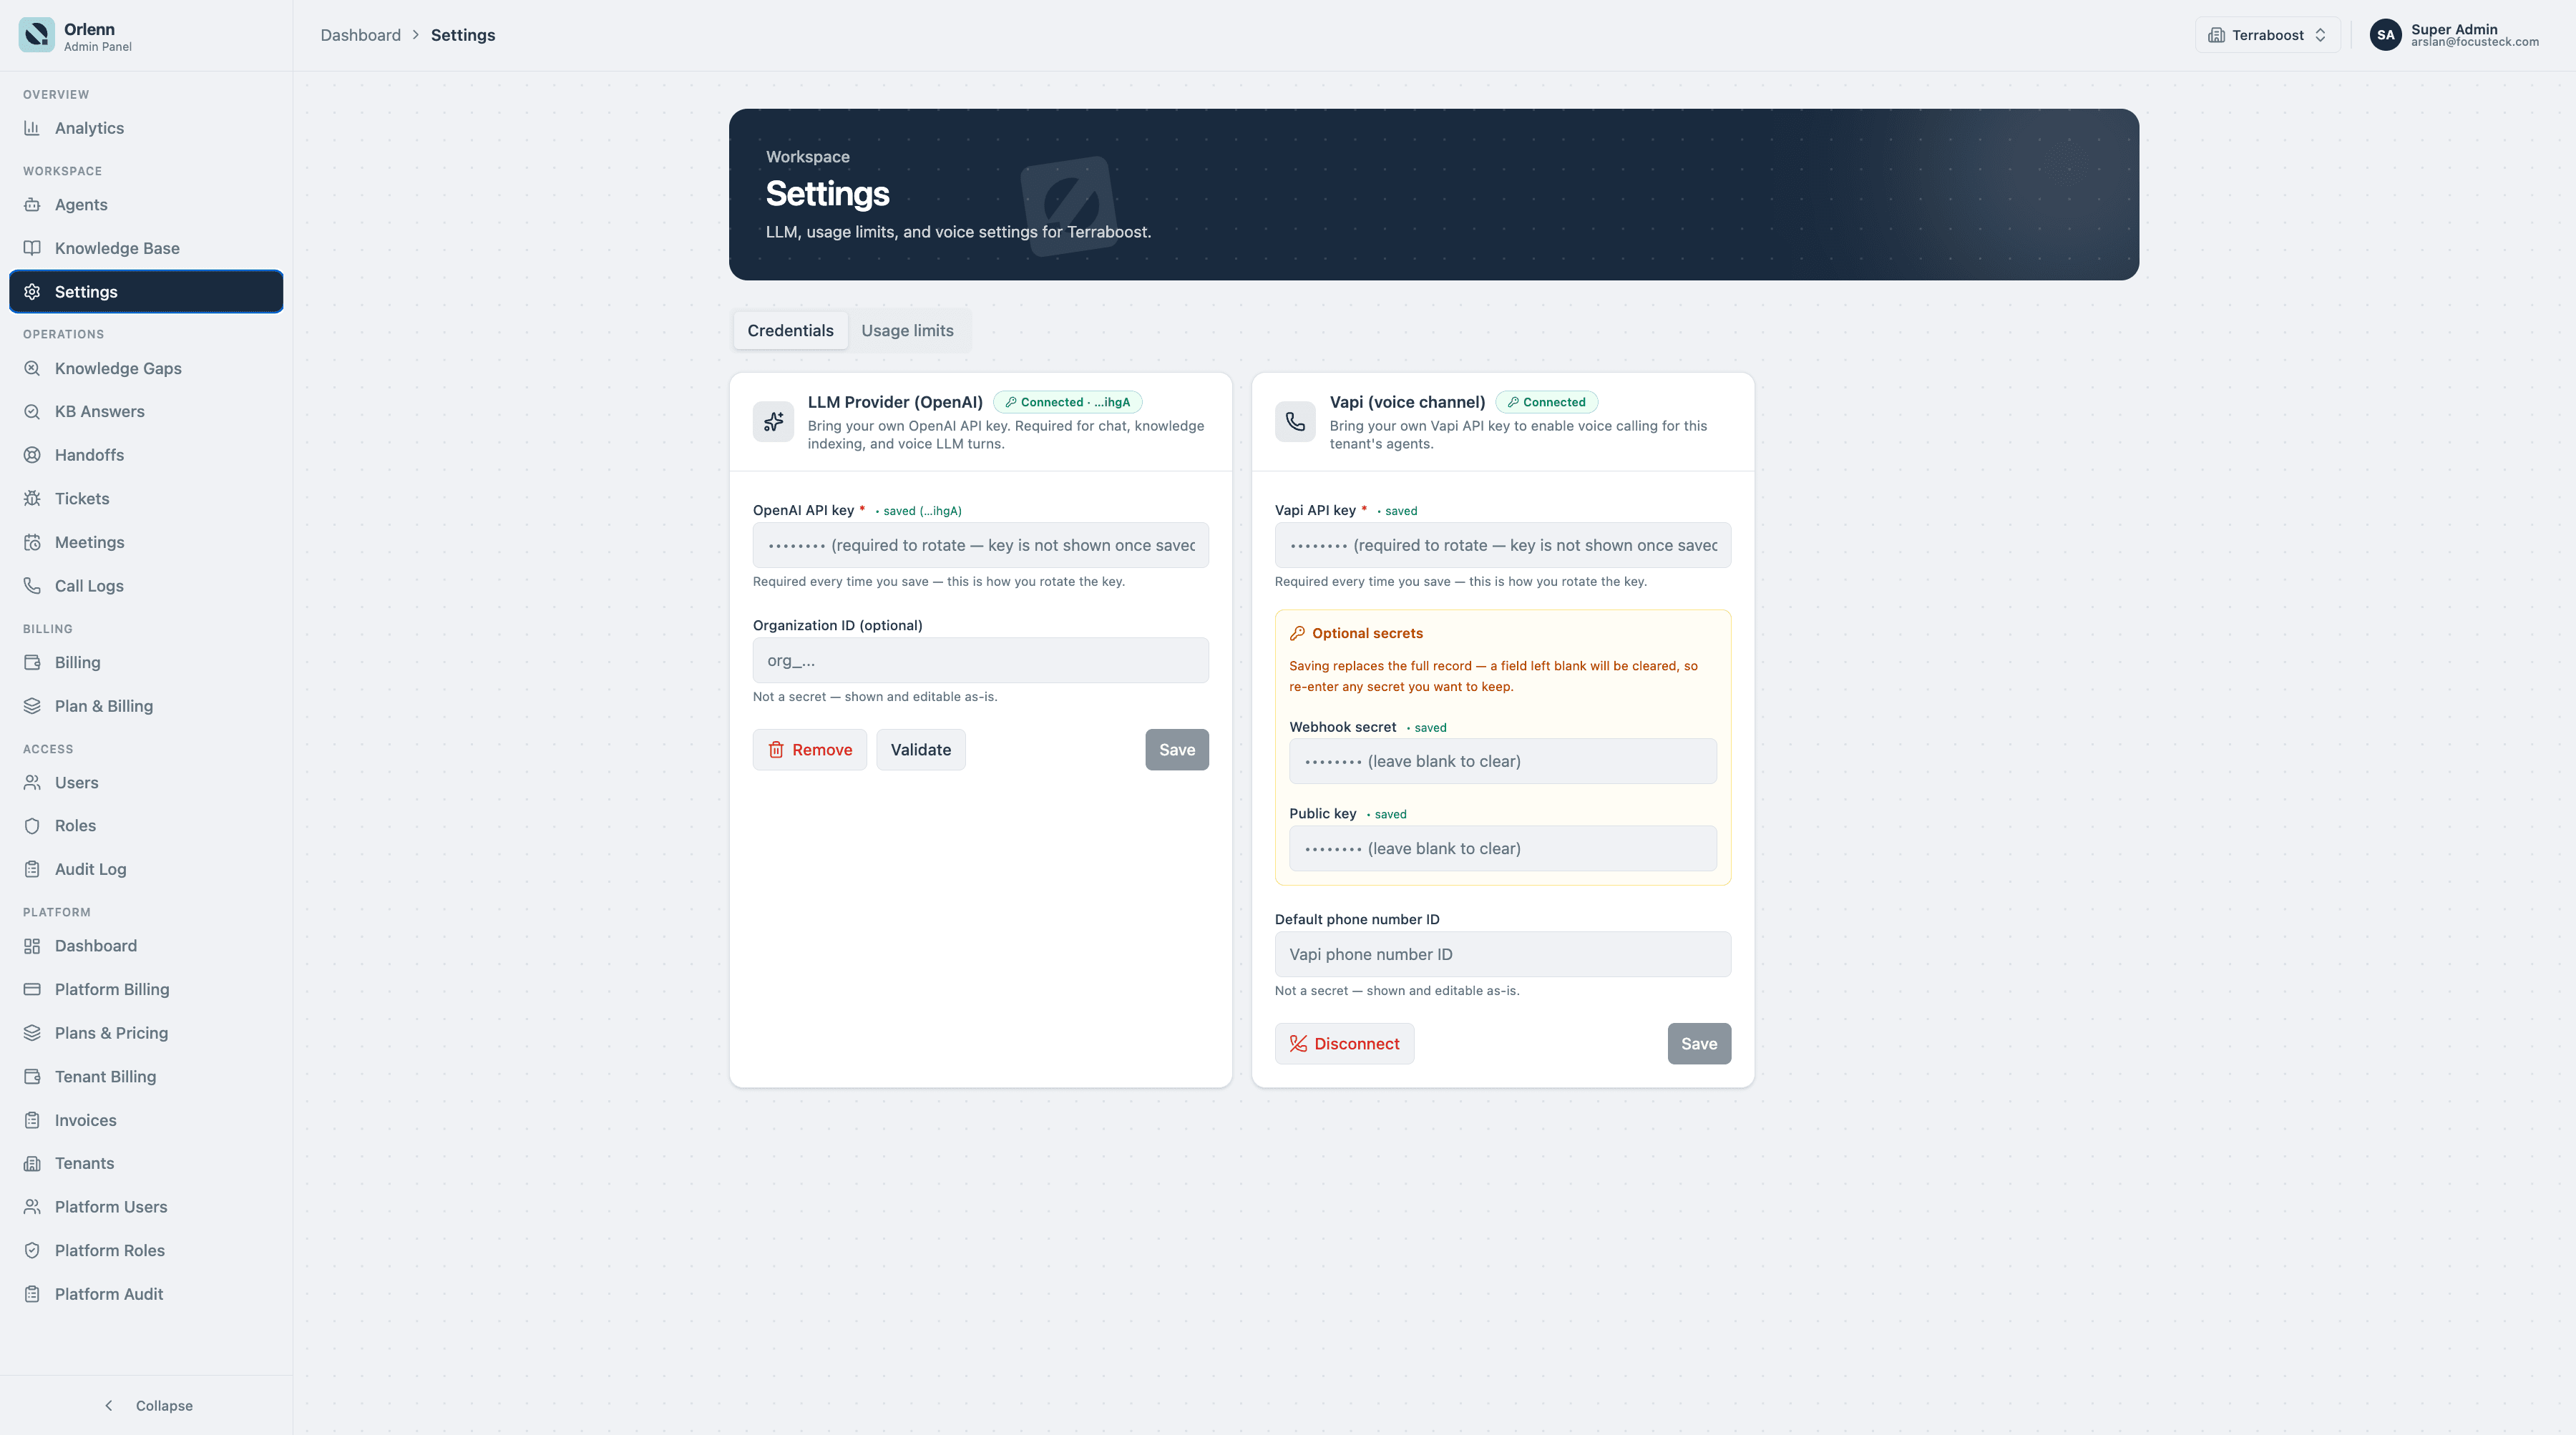
Every tenant supplies its own model key; there is no platform key at runtime.
Orlenn is built to run on public-facing sites and inside businesses that care about their data.
Every tenant supplies its own model key; there is no platform key at runtime.
Integration secrets are stored AES-256-GCM encrypted.
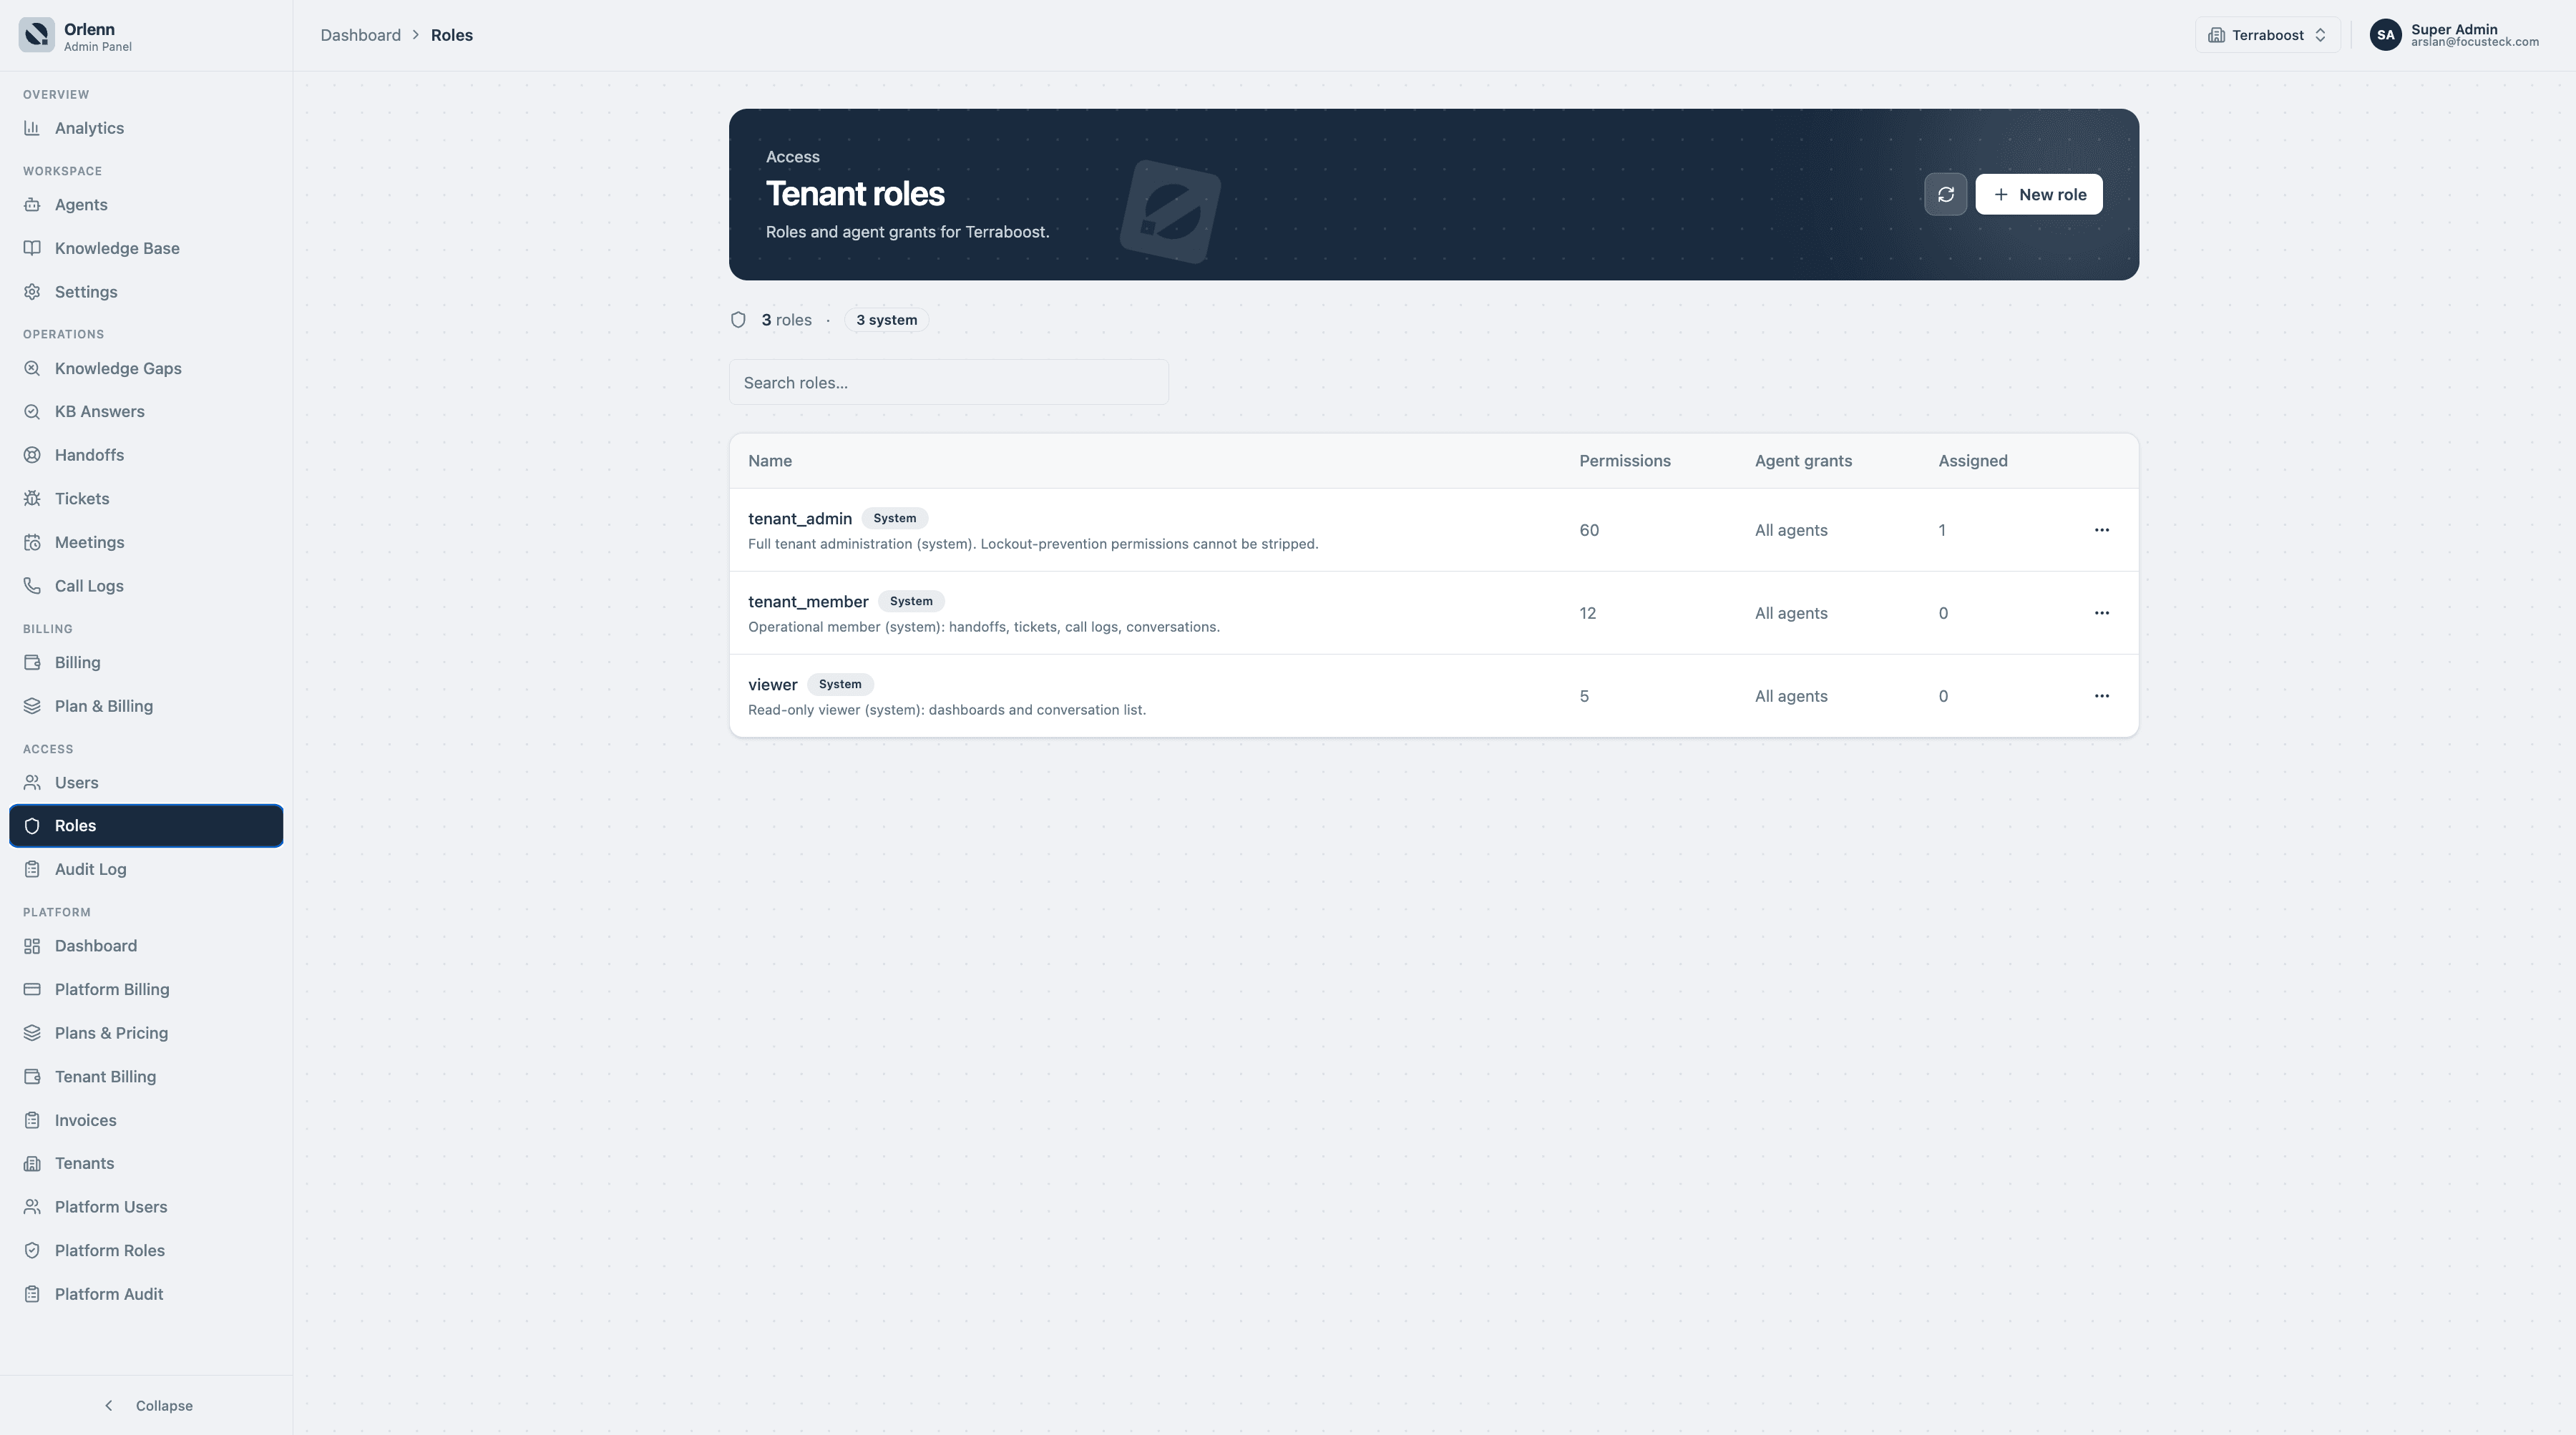
Dynamic role-based permissions, deny-by-default for custom roles, and mandatory 2FA (TOTP).
Every record and credential is scoped to its tenant; tools can't leak across tenants.
Prompt-injection defense, idempotent actions, per-conversation token budgets, and rate limiting on public endpoints.
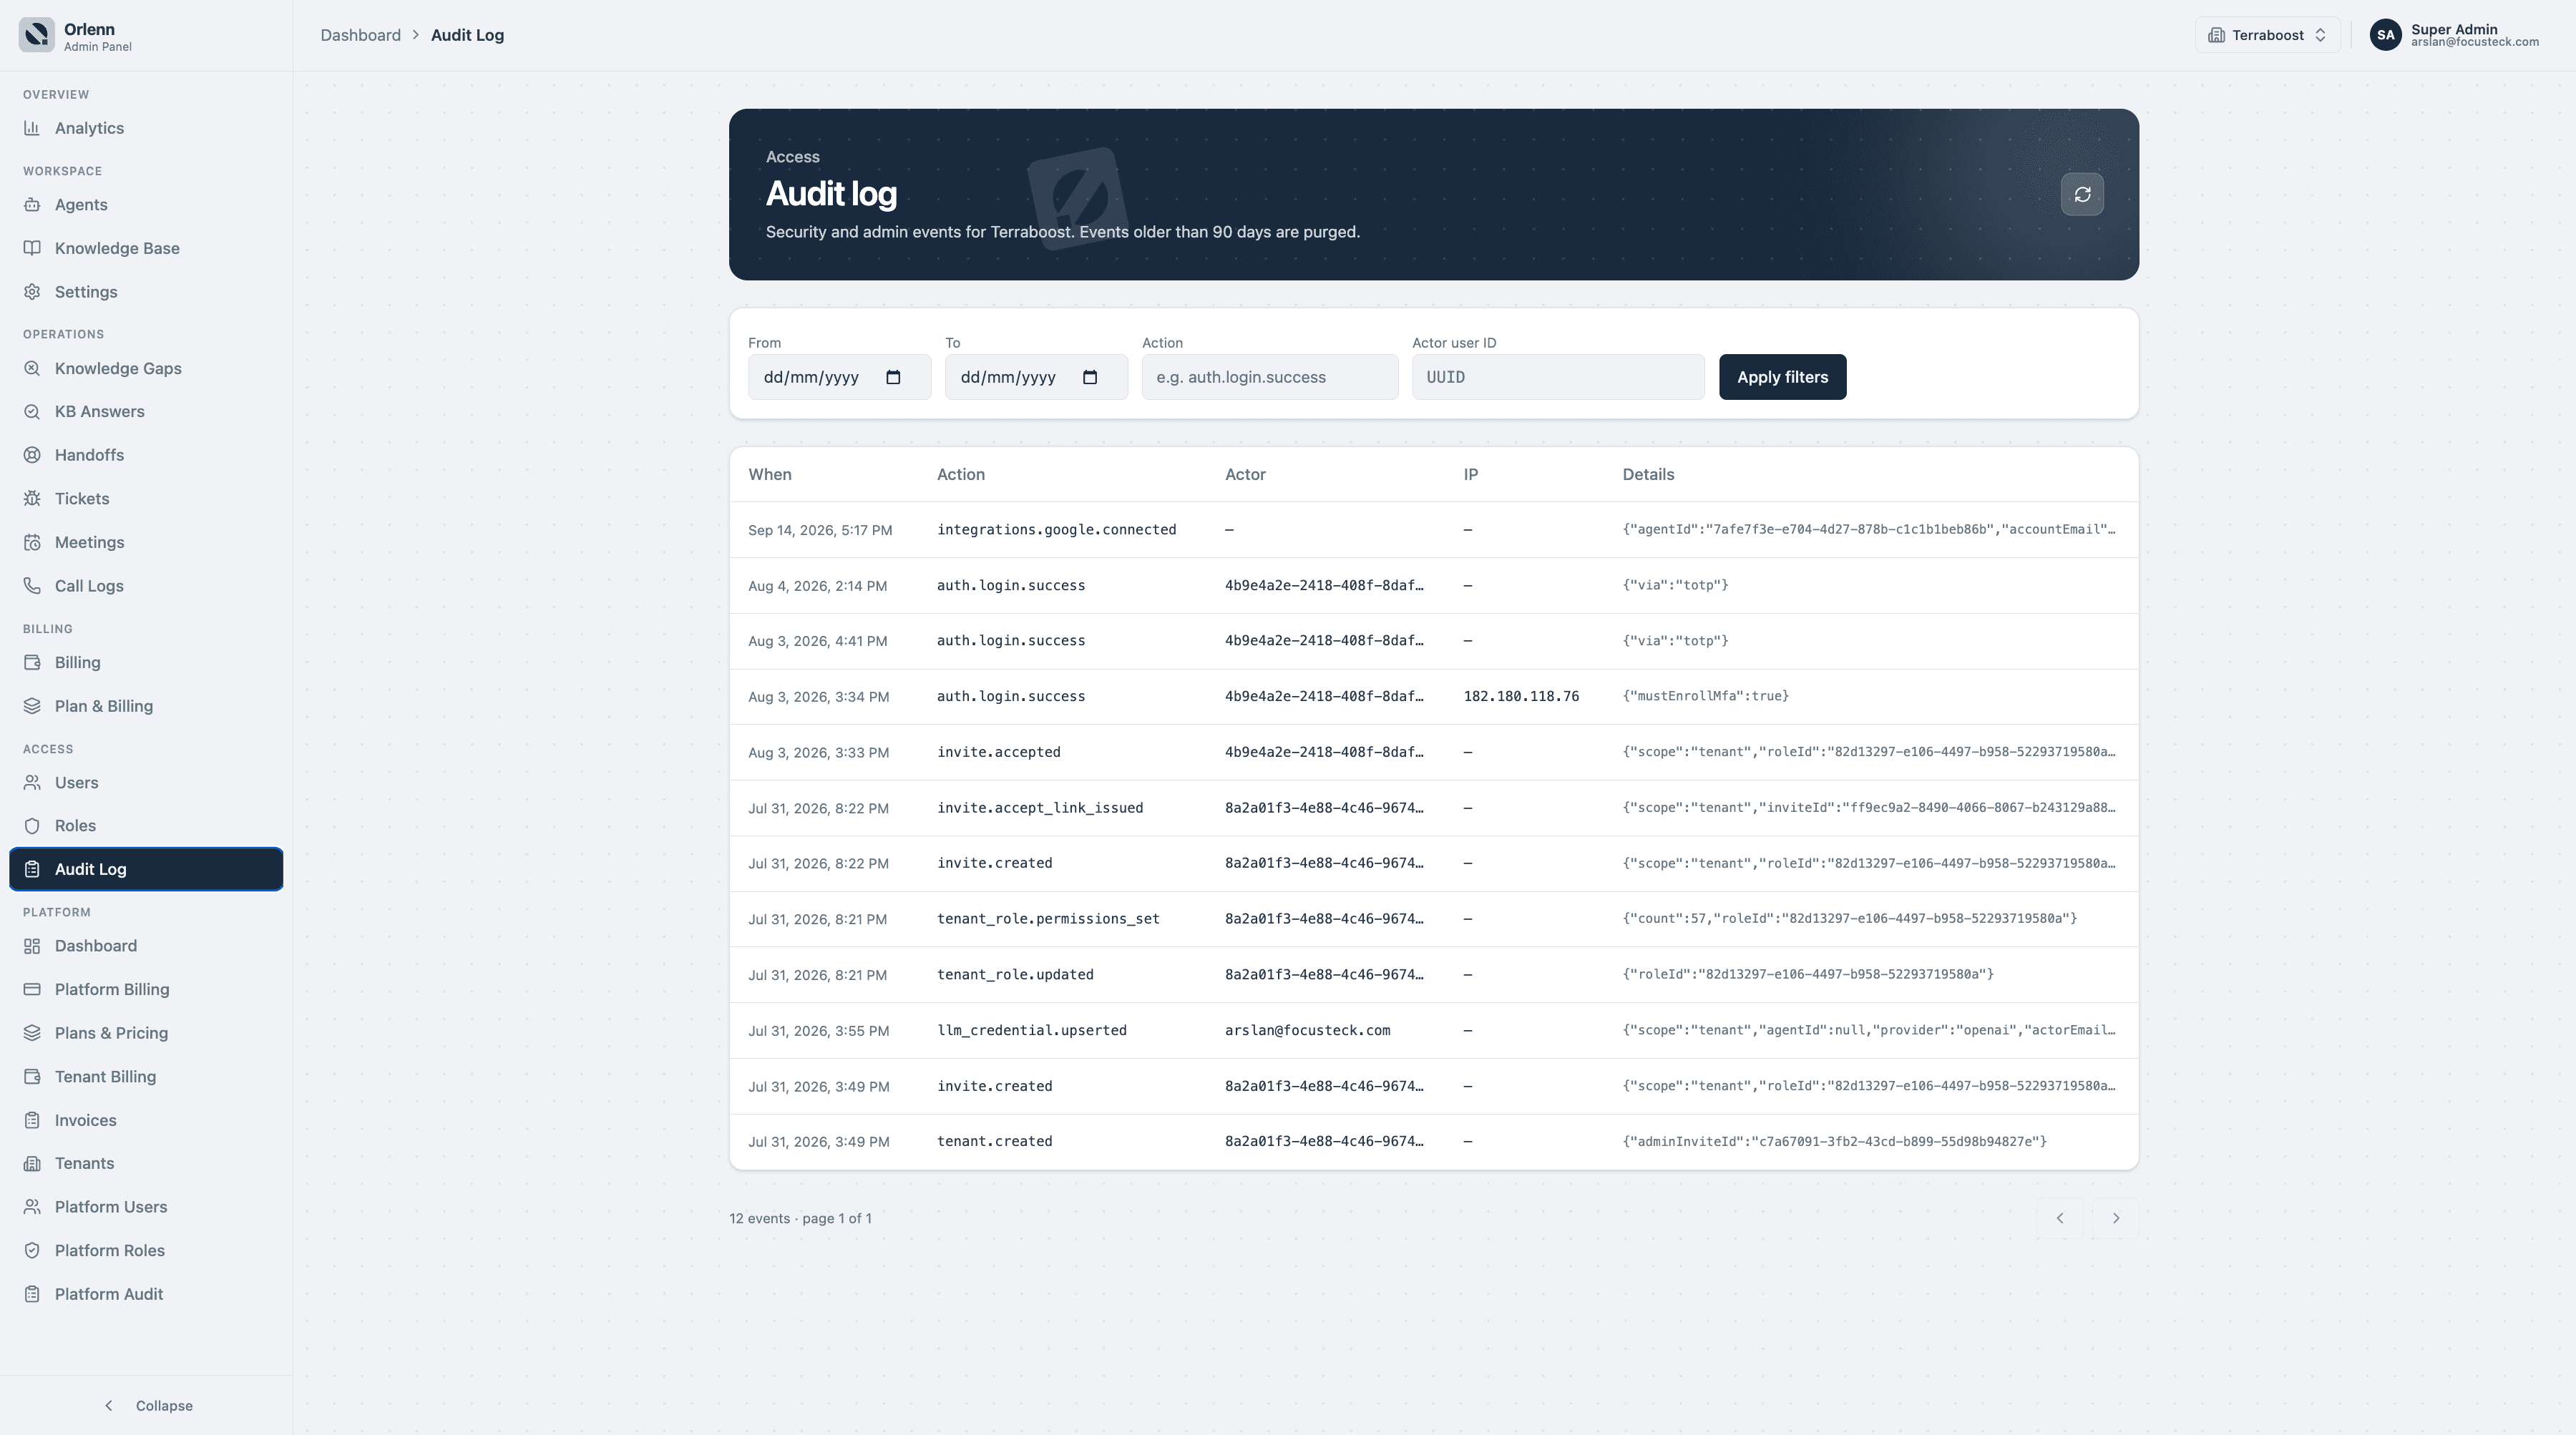
An immutable log records every tool execution and admin action.